Security
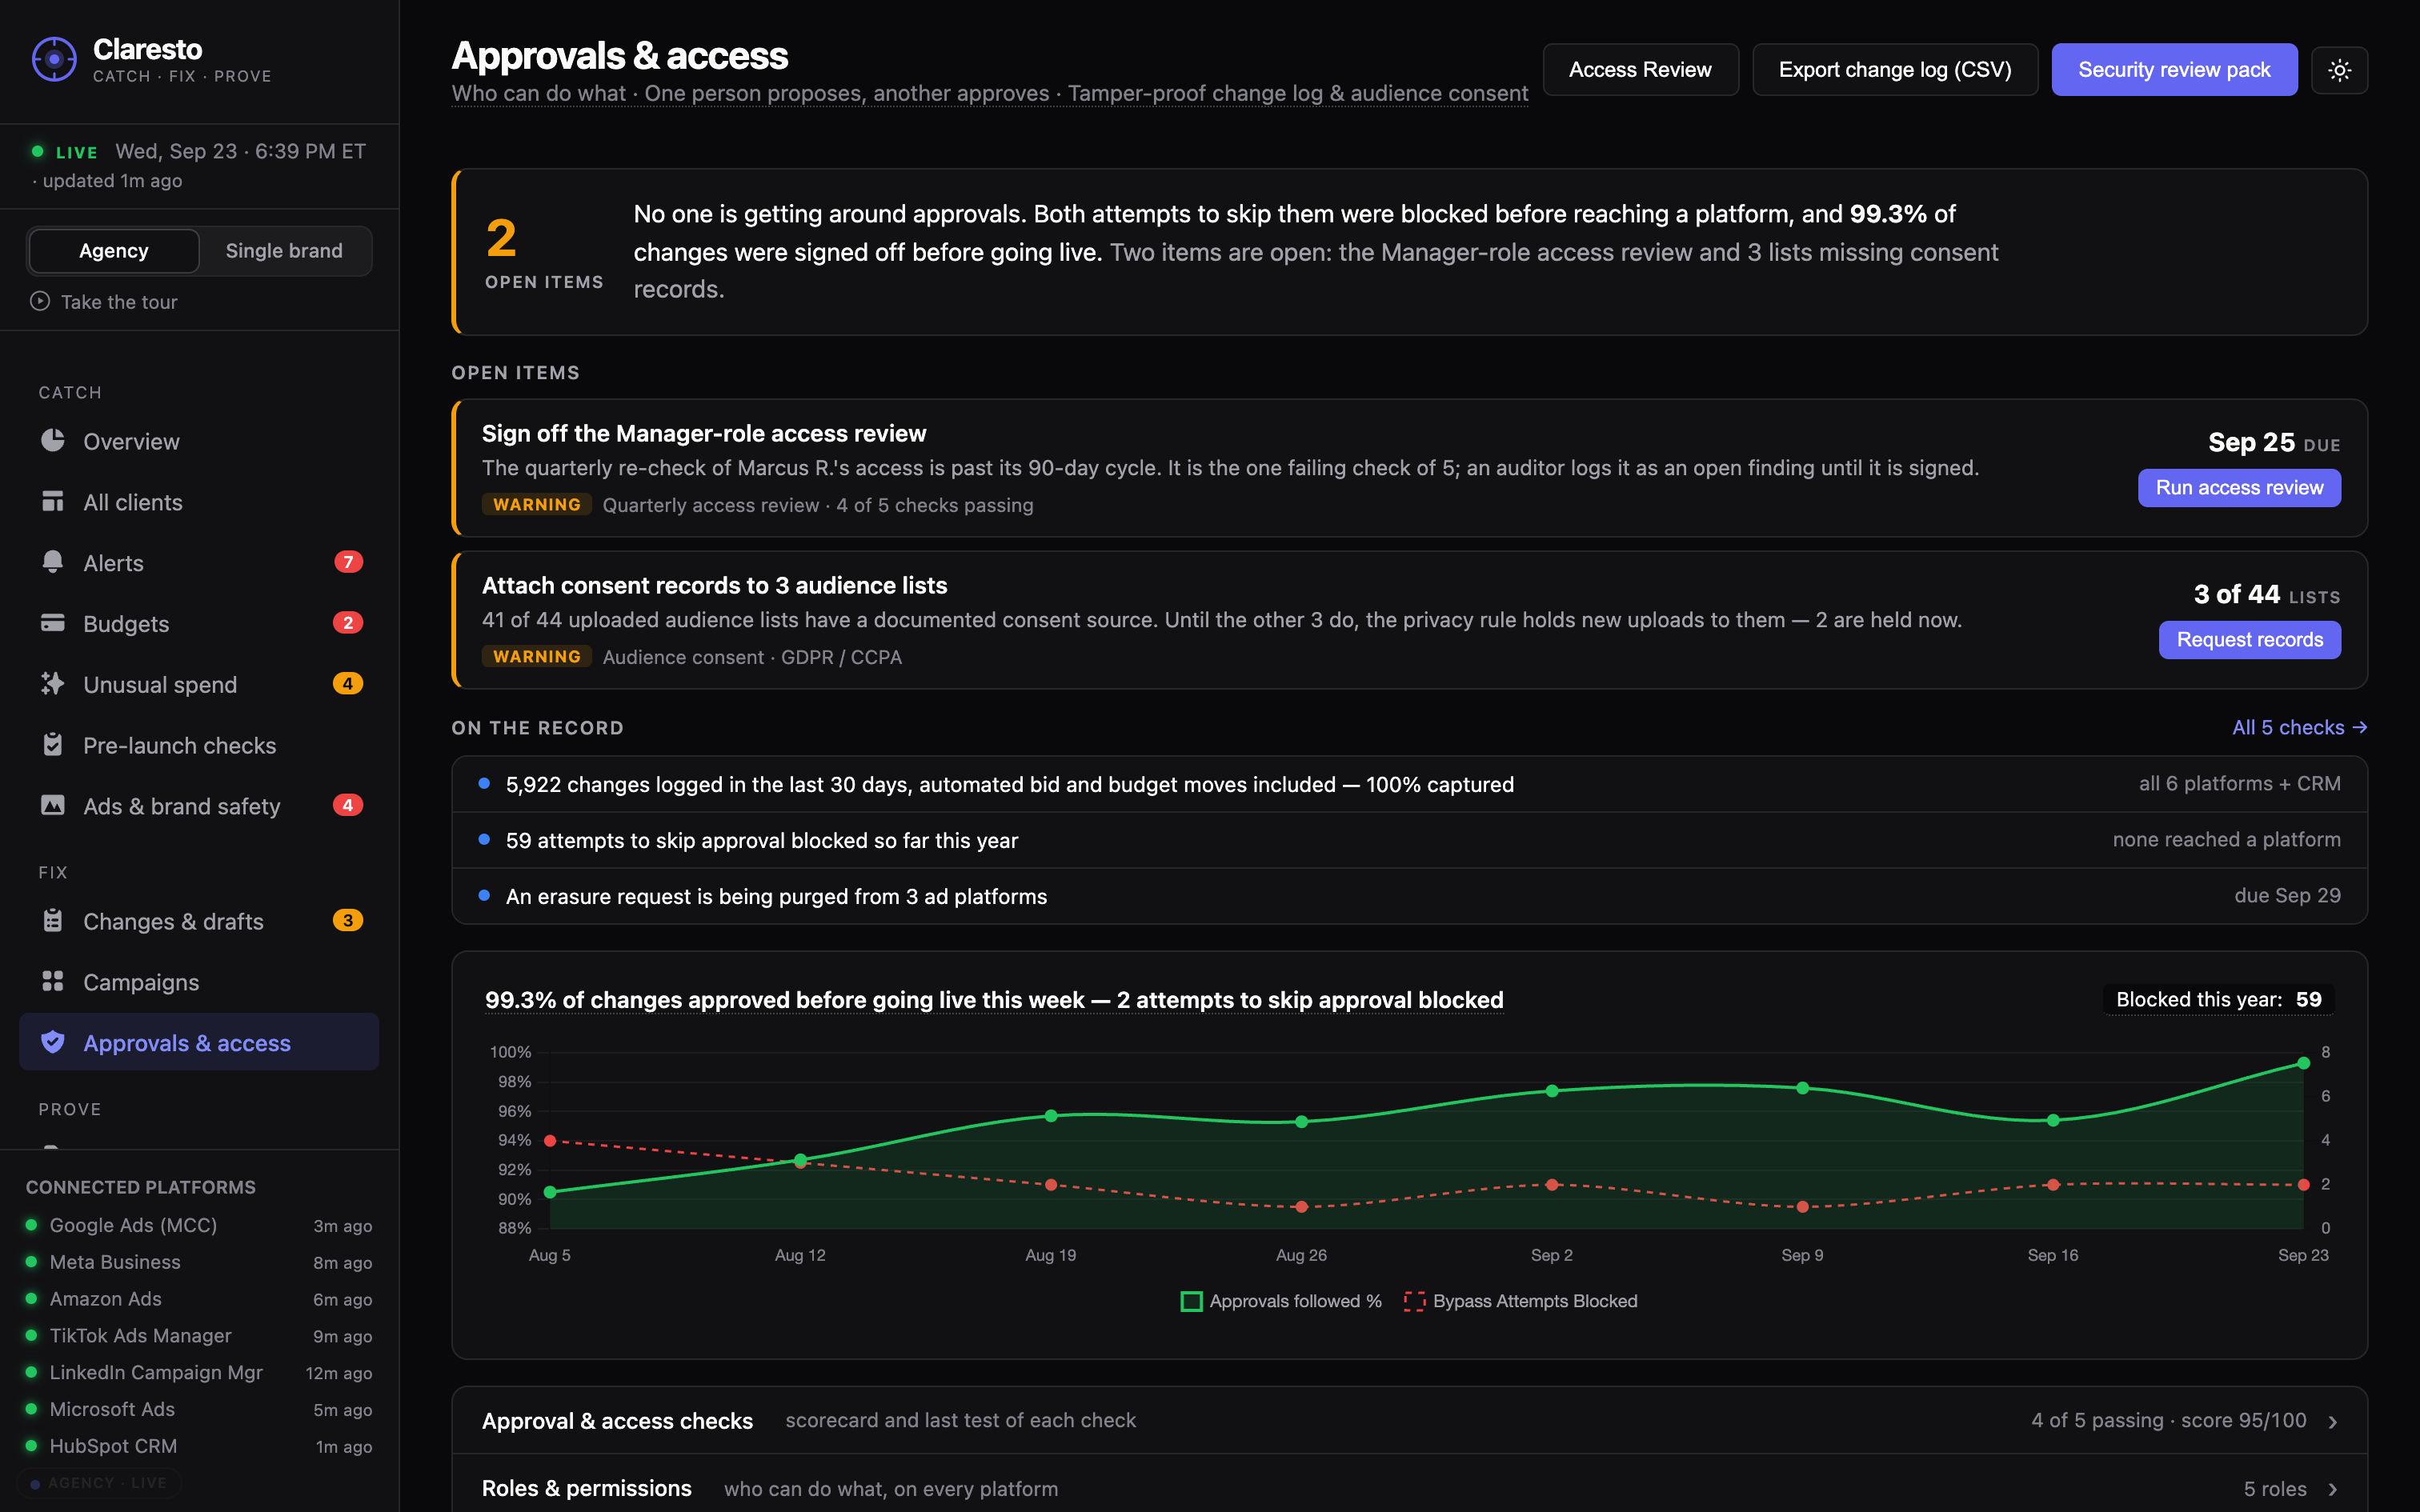
Nothing changes without your approval.
Claresto reads your ad accounts. It never changes anything on its own — a fix goes live only after someone on your team clicks Approve, and every change is logged.
Claresto reads your ad accounts. It never changes anything on its own — a fix goes live only after someone on your team clicks Approve, and every change is logged.
People get the access their job needs, and the person who proposes a change is never the only one who can release it.
Every change across every platform lands in one log you can search and export — not in screenshots.
Claresto only handles the data it needs: campaign settings, spend, conversions, changes, approvals and invoices.
A security pack answers the questions security, finance and procurement teams ask first.
How access works, the permissions we ask for, the change log, and our data processing agreement — ready for your review.